
Glassbox
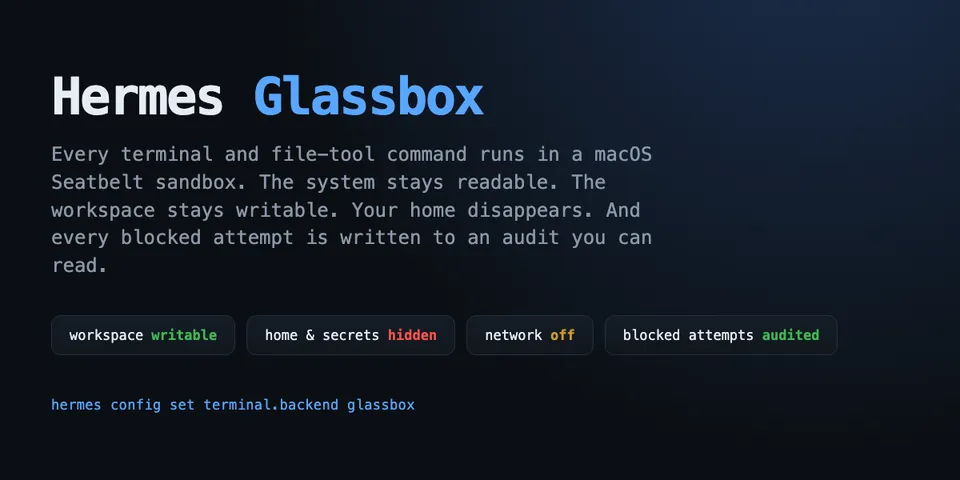
From its catalog listing
A contained, auditable terminal backend for macOS. Select it with `hermes config set terminal.backend glassbox` and every terminal, execute_code, read_file, write_file, patch and search_files call runs under a generated Seatbelt profile: the system stays readable, the workspace is writable, the rest of the user's home is hidden, the home directory itself is never used as the workspace, and network access is off by default. The kernel-refused reads, writes and network attempts are recorded in a local audit log, so "what did the agent try to touch?" is answerable: `hermes glassbox report` (text or a self-contained dark HTML timeline), `/glassbox status|verify|report|profile`, the glassbox_report / glassbox_policy / glassbox_verify tools, a containment self-test (`hermes glassbox verify`: workspace read/write, home read/write denial, child-process confinement, parent traversal, network denial, secret-env filtering) and a one-command demo (`hermes glassbox demo`). A pre_tool_call preflight turns file-tool denials into an actionable error with the exact `hermes config set` line to allow a path, instead of the masked empty read a `2>/dev/null` shell probe would otherwise produce. Settings: network, allow_home, workspace_writable, read_paths, write_paths, deny_paths, audit — apply to the next command, editable from the Desktop Plugins tab.
Good to know before installing
macOS only; runs the agent's shell and file-tool commands on this Mac as the same UNIX user under /usr/bin/sandbox-exec (an OS kernel sandbox, not a VM or a separate UID; it does not defend against a kernel exploit, and system mach services other than Apple Events and LaunchServices stay reachable); osascript, open, security and launchctl are blocked by path, and Apple Events plus LaunchServices mach services are denied; the home directory is never used as the workspace and shell startup files and ~/Library/LaunchAgents are always write-denied; the generated profile, a private scratch home/tmp area and the audit log live under HERMES_HOME/plugin-data/glassbox/ (the audit stores command text truncated to 2000 chars, cwd, exit code, duration, blocked paths and a short output excerpt only when something was blocked — local only, capped at 4 MB with one rotation, never uploaded, `hermes glassbox clear` deletes it); reads the workspace and any extra read_paths/write_paths the user configures; runs two `git config --global --get` calls to copy the Git author name/email into the sandbox environment because ~/.gitconfig is hidden; provider keys, tokens, passwords and SSH agent sockets are filtered from every sandboxed child environment; the containment self-test writes and removes canary files in the home directory; no network calls of its own, no background processes, no telemetry; Seatbelt is marked deprecated by Apple but shipped and functional on current macOS — if a future macOS drops sandbox-exec the backend reports unavailable instead of running unconfined.
From its catalog listing.
How to install
- Install it. Hermes asks for any API keys it needs, then asks whether to turn it on.
hermes plugins install glassbox - Said no? Turn it on later:
hermes plugins enable glassbox - Restart Hermes so it loads the plugin.
Some plugins also need a sign-in or settings: see Full setup & settings. Memory plugins ask whether to become your memory provider instead. Steps follow the official plugins guide (opens in a new tab).
- Category
- Coding & developer tools
- Maintained by
- rkfshakti (Community)
- Needs
- No API keys declared
- Adds tools
glassbox_reportglassbox_policyglassbox_verify- Adds hooks
pre_tool_call- Works on
- macos
- Needs Hermes
- 0.22.3 or newer
- Version
- 1.1.0
- In the catalog
- 2026-11-11
Known issues (from its catalog listing)
- Seatbelt is a deny-by-default OS sandbox, not a virtual machine: commands run as the same user, and the plugin does not defend against a kernel exploit or against a process the user deliberately launches outside the sandbox.
- Commands that need network (package installs, git push over HTTPS) require `network: true` or a local mirror; SSH agent sockets and ~/.ssh are never passed in.
Using the Hermes desktop app? See where plugins live

Full setup & settings ↗Source code ↗
More in coding & developer tools
All coding & developer tools plugins
New Hermes Agent updates every day on X. Follow @HermesWatcher